Problem
Supplier data lives in 6 different spreadsheets across 3 departments
SustainGRC
Single canonical supplier register — collect once, use everywhere
Assurance Without Limits: Rethinking QAIP - 7 October
From Tier 1 to Tier 3+. Supplier mapping, ESG risk discovery, due diligence automation, and continuous governance — connected to your broader GRC and sustainability infrastructure.
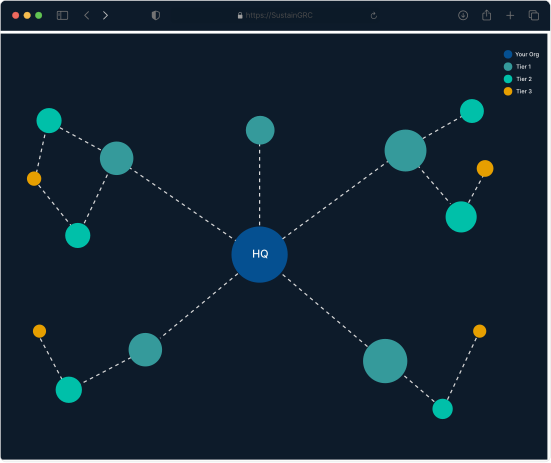
Most organisations know their Tier 1 suppliers. Regulators now demand visibility all the way down.
Supplier data lives in 6 different spreadsheets across 3 departments
Single canonical supplier register — collect once, use everywhere
CSDDD requires Tier 2+ visibility but you only know Tier 1
Multi-tier mapping with relationship chaining and gap detection
Questionnaires sent via email with no audit trail
Governed workflows: sent, chased, scored, evidenced, and logged
No connection between supplier risk and enterprise risk posture
Supply chain risks flow into the unified risk register automatically
From initial mapping through to continuous governance — a complete, connected workflow
Tier 1 → Tier N visibility
Build a living map of your entire supply network. Auto-classify suppliers by tier, criticality, spend, and geography — then overlay ESG risk signals from across the platform.

Multi-tier relationship mapping (Tier 1 to Tier 3+)
Auto-tiering based on spend, dependency, and criticality
Geographic concentration heat mapping
Critical supplier identification and single-source flagging
Tiers deep
A continuous governance cycle — not a one-off exercise.
Upload supplier data or connect via API. Auto-tier and map relationships.
Deploy ESG questionnaires. Score responses. Link evidence.
Continuous risk scanning. Real-time alerts on material changes.
Board packs, framework disclosures, and remediation tracking.
Connected Intelligence Supply chain governance doesn't live in isolation. Every module feeds and is fed by your broader platform.
Predictive risk trajectory scoring for every supplier
UNGP and OECD-aligned salient issue assessments
Scope 3 upstream emissions from supplier data
GRI 308/414 disclosures auto-populated
Supply chain risks feed the unified risk register
Supplier emissions data for border adjustment
Supplier data collected once feeds GHG Scope 3, HRDD assessments, CBAM declarations, and framework disclosures — no duplicate entry, no reconciliation.
Built to meet the supply chain due diligence requirements you're being asked about today.
CSDDD
Corporate Sustainability Due Diligence Directive
LkSG
German Supply Chain Due Diligence Act
UK MSA
UK Modern Slavery Act
GRI 308
Supplier Environmental Assessment
GRI 414
Supplier Social Assessment
EUDR
EU Deforestation Regulation
InsightLens follows our foundational principle for AI in governance and compliance.
InsightLens surfaces insights, identifies gaps, and recommends actions based on your governed data.
Every recommendation requires human review and approval. No autonomous decisions on governance matters.
Complete audit trail of queries, responses, confirmations, and actions. Full regulatory defensibility.