01
70%+
Faster Data Collection
Assurance Without Limits: Rethinking QAIP - 7 October
Manage enterprise and cyber risk, run internal audit, test controls, govern AI, withstand disruption and report on sustainability.One AI-native system of record.
Trusted by organisations that govern seriously


SustainGRC turns fragmentation into orchestration — breaking down silos and bringing every team across the organisation onto one system of record.
Governance Intelligence Infrastructure
Unlike tools that force organisations to choose between ESG or GRC solutions, SustainGRC governs non-financial data integrity across ESG, risk, audit, and supply chains — enabling assured reporting, regulatory confidence, and decision-grade insight.
From GHG inventory to CSRD disclosure, TCFD and EU Taxonomy — manage every sustainability obligation on one data model. Assured reporting, audit-ready, every cycle.
Learn moreWHY WE WIN
40+ modules on one canonical data model. Not 10 acquisitions stitched together. Enter once, serve everywhere.
Financial-grade validation from source to report. Anomaly detection, multi-source reconciliation, complete audit trails.
Material topics feed risk registers. Carbon data populates disclosures. Regulatory changes propagate platform-wide.
When regulators ask how you govern non-financial data, your answer is either the platform or a folder of spreadsheets.
Built on Azure's sovereign cloud infrastructure with encryption at rest (AES-256) and in transit (TLS 1.3). Penetration-tested quarterly by independent CREST-certified assessors.
ISO 27001Every AI recommendation carries a deterministic audit trail. Human confirmation gates enforce separation of duties. No black-box scoring — every output is explainable, challengeable, and court-admissible.
EU AI Act AlignedDeploy in UK, EU, GCC, or APAC regions with full data residency guarantees. Tenant-isolated architecture means your data never co-mingles. GDPR, PDPL, and NDMO compliant from day one.
Multi-JurisdictionalWrite once, read many audit logs with SHA-256 integrity seals. State machine enforcement (DRAFT → IN_REVIEW → APPROVED → LOCKED) ensures no record is altered without a traceable, justified override.
WORM Audit TrailRole-based access with enforced SoD — the person who creates a record cannot approve it. Board-level permissions cascade through every module. No admin backdoors.
Separation of DutiesAzure-hosted with geo-redundant failover, automated backups every 15 minutes, and a contractual SLA backed by financial penalties. Disaster recovery tested monthly, not annually.
99.9% SLATrusted where non-financial data
must stand up to scrutiny.
"SustainGRC is a genuinely complete platform. The integration between GRC and ESG is a strong differentiator — risks link directly to ESG indicators and surface immediately in reports and dashboards. The AI-driven orchestration across modules and data sources brings a level of automation to evidence collection and data quality I haven't seen in comparable solutions."

André Cangussú
Internal Audit Leader, Klabin
"We've been evaluating integrated GRC + ESG platforms for a while, and SustainGRC's Intelligence Hub stands out as the most comprehensive solution we've seen. The unified approach to sustainability data management and the financial-grade intelligence capabilities align perfectly with what we need for our renewable energy business in Qatar. We're excited about the potential to transform our ESG practice from manual processes into strategic business intelligence."

Ammar Abdelghani
Solar Department Manager - FTC Qatar
"I was truly impressed by SustainGRC's Al-powered carbon calculation and integrated sustainability platform. The insights it provided were incredibly valuable, the results far surpassed my expectations, and the team behind it was exceptionally friendly. I wholeheartedly recommend SustainGRC to anyone looking for innovative sustainability solutions."

Mike Oaten
CEO at Tikos - building trustworthy Al
"Dr. Ahmed is a dedicated advocate for sustainable development and ethical business practices through SustainGRC . His expertise and commitment to making a positive impact are inspiring, and his ability to empower individuals and enterprises to embed ethical practices is commendable. We need more leaders like him who are driven by purpose."

Samer Jannoun
Head of Regional Ethics & Compliance @Meta
Connected Governance
SustainGRC connects governance, risk, internal audit, sustainability and supply chain on a single data model — so every framework, every filing and every sign-off draws from one source of truth. Built as one.
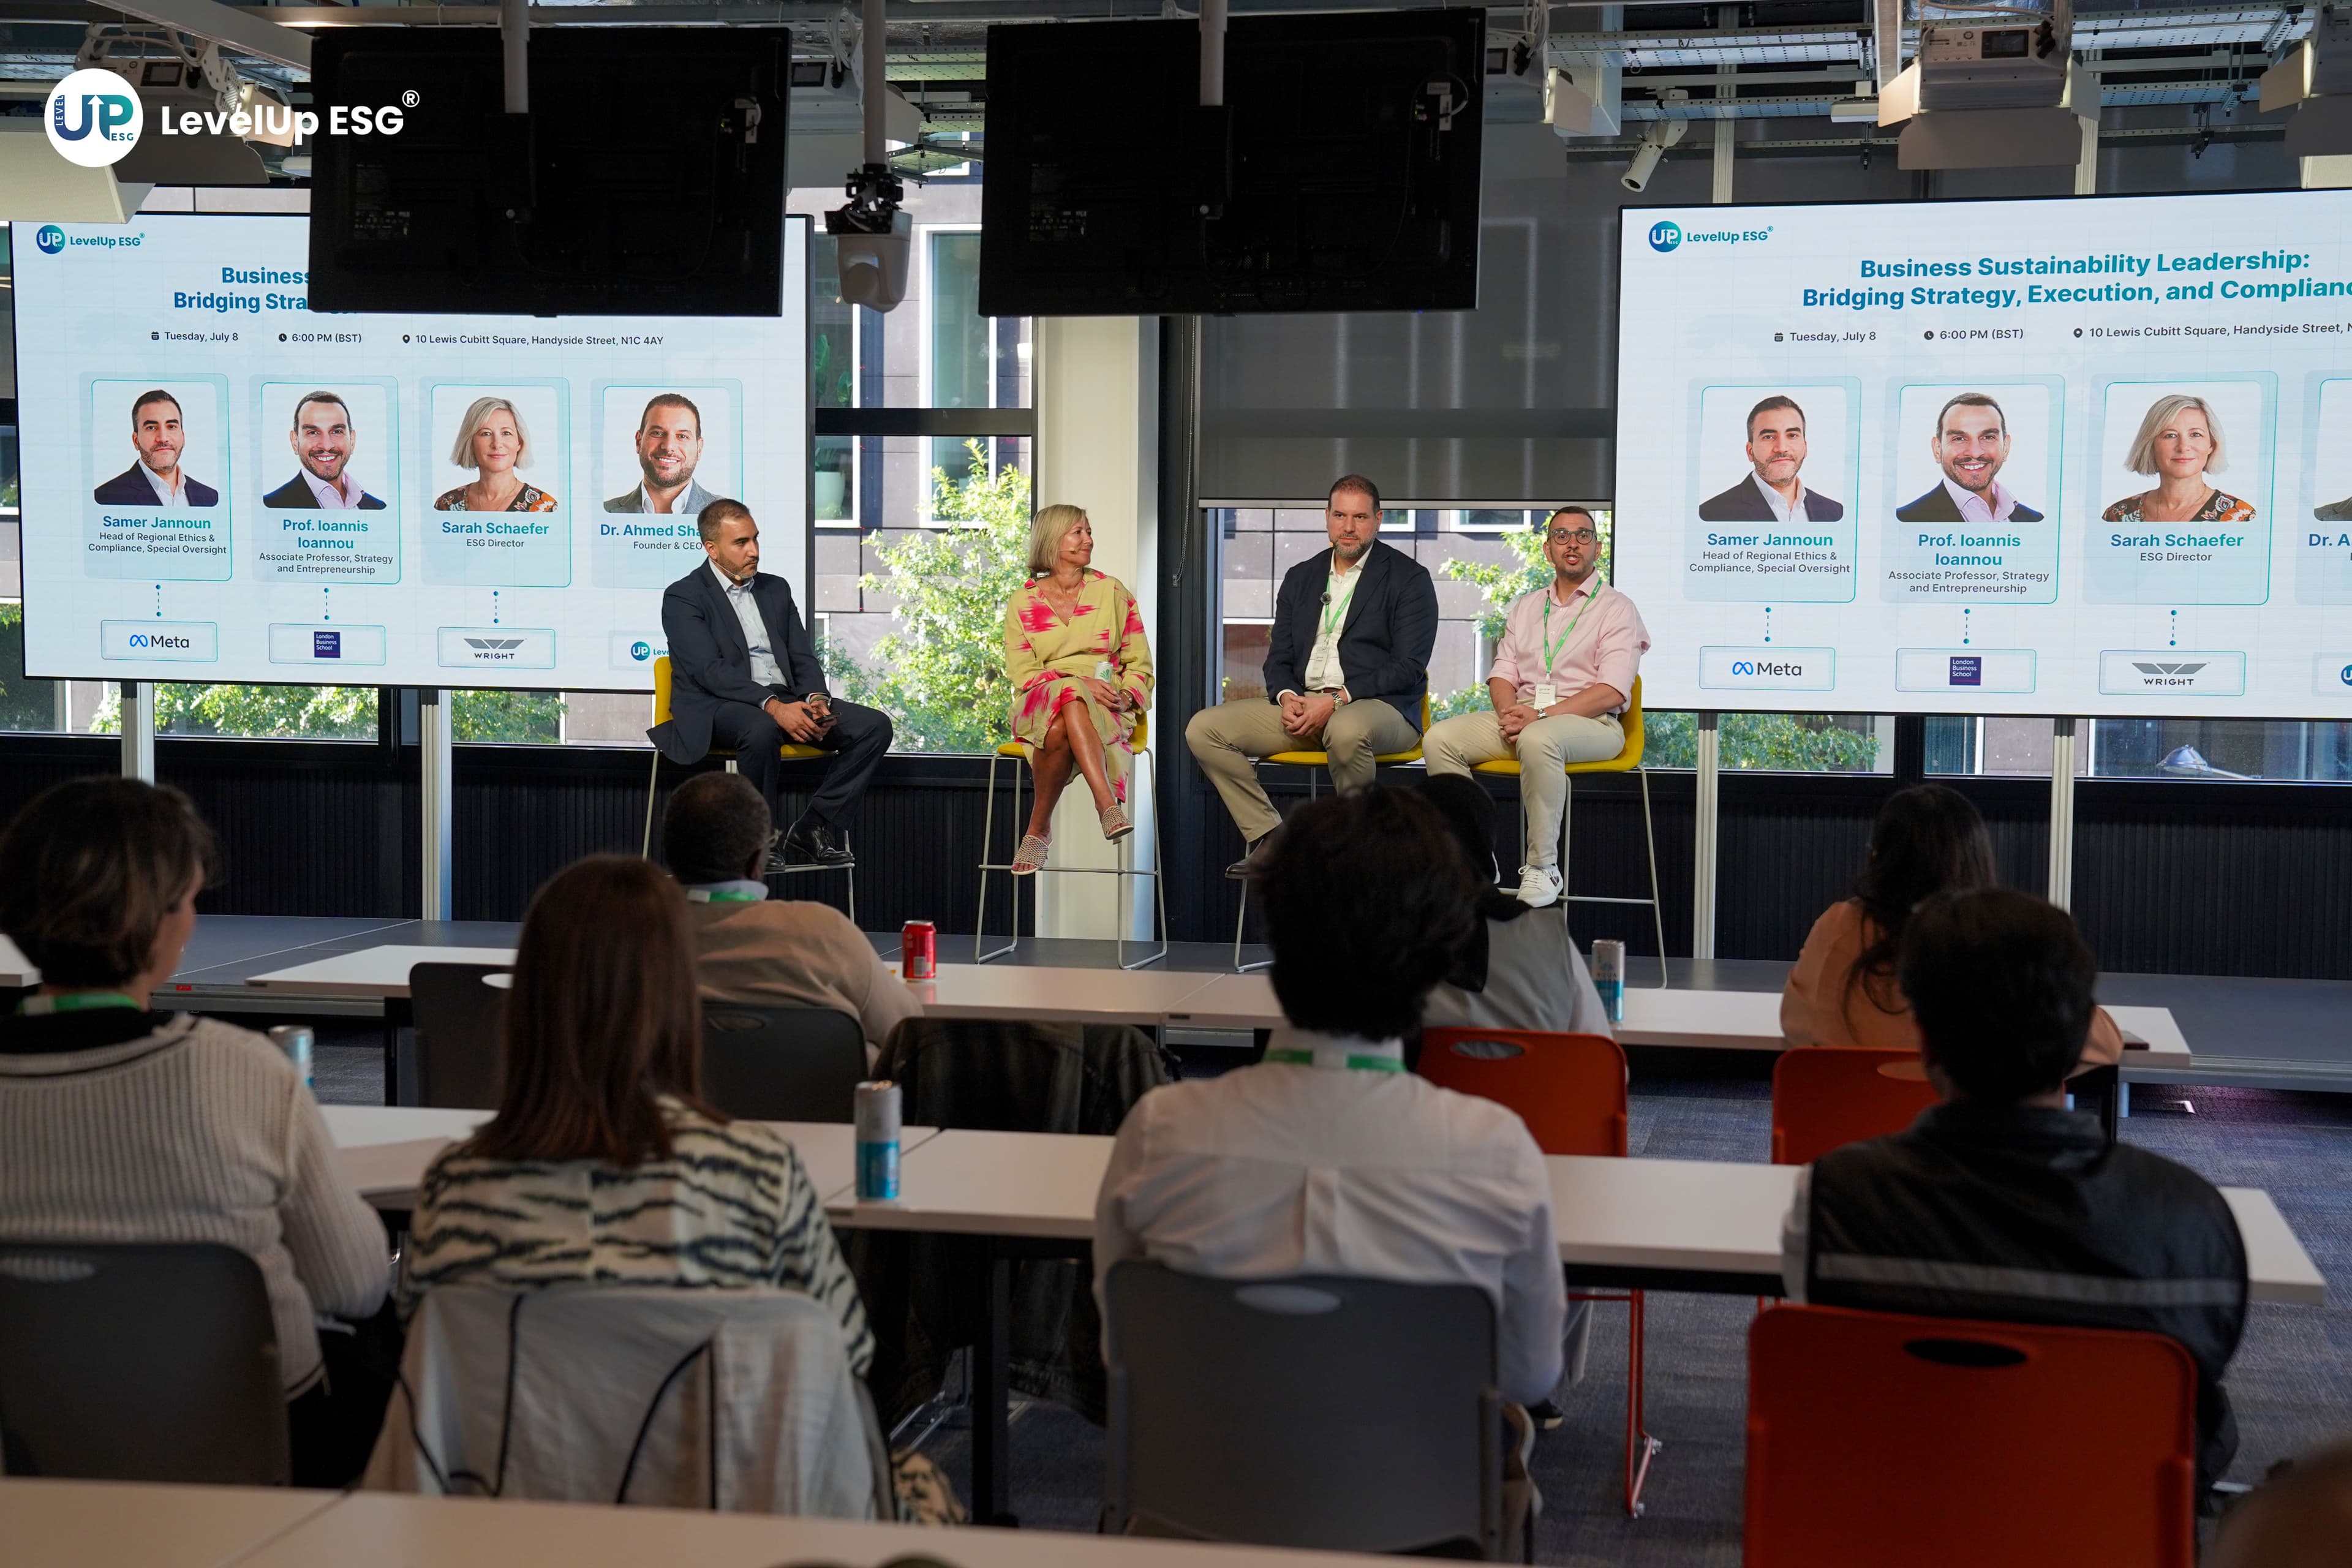
From product to presence we're part of the conversation
Reduced Scope 3 reporting cycle from 3 months to 3 week using AI-native automation for data capture, validation, and workflow orchestration.
Enhanced stakeholder confidence with investor-grade, audit-ready emissions reporting.
Embedded ESG-aligned investment screening across $5bn portfolio ensuring IFC-compliant risk and governance integration in every decision.
Strengthened oversight with evidence trails and alignment to global sustainable finance guidelines.